

SANKET संकेत
Secure messaging app and sovereign secure communication platform
Your data. Your Control. Your Ownership.
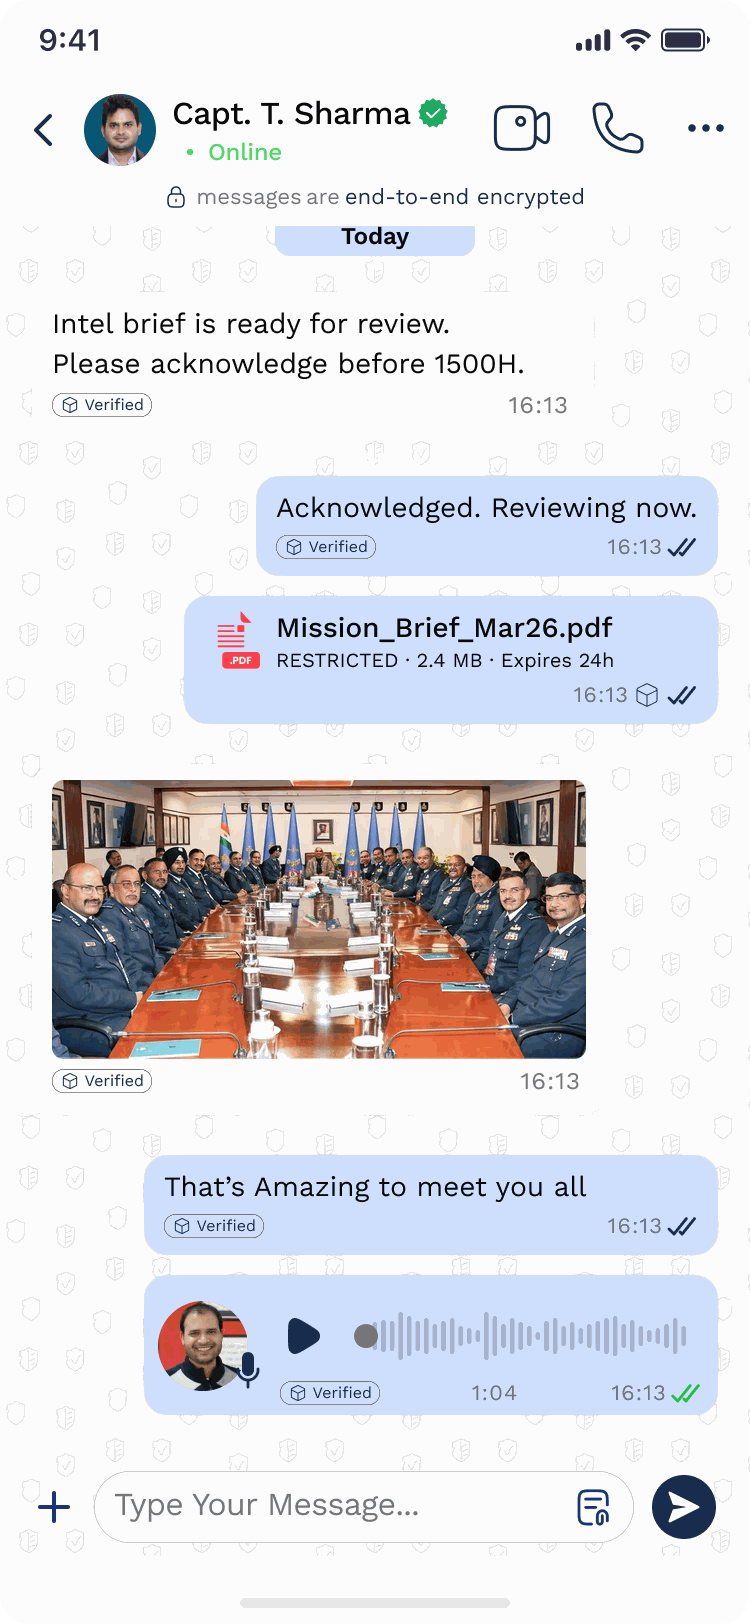
SANKET (Sanket.Chat) by Tosh Defence gives defence, government and high-trust organisations end-to-end encrypted messaging, file exchange, voice and video calls and priority broadcast, built on Signal's independently audited libsignal with post-quantum protection and AES-256, on infrastructure you control, from your chosen cloud to a fully air-gapped network.




What is Sanket
SANKET (Sanket.Chat) by Tosh Defence is a defence-grade, sovereign secure communication platform for defence forces, government departments, intelligence and law-enforcement agencies, critical infrastructure operators and other organisations whose communications must stay confidential even if the network or the hosting provider cannot be trusted.
What this means
संकेत means "Signal" in English
संकेत (SANKET) - Signal. Code. Indication. Covert sign. Used in military contexts for covert signals between forces. The word IS communications - warm, approachable, and unmistakably Indian.
MADE IN INDIA. FOR INDIA. FOR THE WORLD.
A Sovereign Alternative to Consumer Messengers and Foreign Collaboration Suites
SANKET is built in India by Tosh Defence for organisations that need defence-grade communication without handing their infrastructure, keys, logs or policy to an outside party. Run it as a dedicated hosted installation, operate it on your own servers, or take it fully air-gapped.
Your Data
Messages, files and calls are end-to-end encrypted, and the server never holds the keys to read them. Every record the server keeps stays inside the installation you choose.
Your Control
Your infrastructure, your identity provider, your policies, your retention and your update timing. Control that hosted messaging services are simply not built to offer.
Your Ownership
One dedicated installation per organisation, with your branding, your certificate authority and your audit trail.
Defence-Grade Security
libsignal with post-quantum protection, AES-256 throughout, hardware-backed keys, signed device lists, device mutual TLS and FIDO2 administrator keys.
THE PROBLEM
High-trust organisations still run critical conversations on consumer messengers and foreign SaaS platforms they neither own nor control. Encryption alone does not answer who operates the service, where it runs, who holds the keys and logs, or who decides when it changes. SANKET answers every one of those questions inside your own security boundary.
THE SOLUTION
What SANKET Does
SANKET (Sanket.Chat) by Tosh Defence is a defence-grade, sovereign secure communication platform for defence forces, government departments, intelligence and law-enforcement agencies, critical infrastructure operators and other organisations whose communications must stay confidential even if the network or the hosting provider cannot be trusted.
SANKET is offered three ways on one platform and one security design: Sanket.Chat, the free public app for iOS and Android; Sanket.Work, a dedicated whitelabel installation hosted in any region on any cloud you choose; and Sanket.Enterprise, operated by you on-premise or fully air-gapped. Its defining advantage is the depth of customer control: your infrastructure, your keys, your identity provider, your policies, your branding, your retention and your update timing.

CAPABILITIES
Key Features
End-to-End Encryption, Post-Quantum Ready
Signal Protocol through Signal's official libsignal: PQXDH key agreement with a Kyber prekey and the Double Ratchet with SPQR. Every message gets a fresh key, and the server never holds the keys to read it.
Secure Voice and Video Calls
One-to-one and group calls with AES-256-GCM frame encryption plus SRTP AES-256-GCM, five new keys every second, tuned for constrained links and able to work over HTTPS port 443.
Encrypted Priority Broadcast
End-to-end encrypted broadcasts at four priority levels, with full-screen alerts, acknowledgement tracking and automatic follow-up for urgent messages not acknowledged in time.
Customer-Defined Classification Labels
Up to eight ranked labels that you define, carried inside the encryption. Content above the lowest rank cannot be forwarded, exported or downloaded, and a forward never lowers a label.
Administrator Security Keys and Your Own SSO
FIDO2 security keys for administrators, sign-in through your own OIDC or SAML 2.0 identity provider, LDAP directory checks and SCIM 2.0 provisioning.
Device Trust Built In
Hardware-backed keys on every phone, device mutual TLS with certificates under your own CA, signed device lists, lost mode and server-confirmed remote wipe.
Sovereign and Air-Gap Capable
One dedicated installation per organisation, on infrastructure you choose, with high availability and second-site recovery. No third-party analytics in any app or server.
Signed Releases You Control
Ed25519-signed releases with freeze and rollback protection, verified before install and installed only when you approve, with automatic rollback if an upgrade fails.
MULTILINGUAL SUPPORT
Built for India's Languages and the World's
Officers, officials and staff use SANKET in their own language, with the interface localised across major Indian and global languages.
हिन्दी
Hindi
বাংলা
Bengali
தமிழ்
Tamil
తెలుగు
Telugu
मराठी
Marathi
ગુજરાતી
Gujarati
ಕನ್ನಡ
Kannada
മലയാളം
Malayalam
ਪੰਜਾਬੀ
Punjabi
ଓଡ଼ିଆ
Odia
অসমীয়া
Assamese
English
English
Français
French
Deutsch
German
Español
Spanish
Português
Portuguese
Русский
Russian
日本語
Japanese
한국어
Korean
中文
Chinese
ไทย
Thai
Tiếng Việt
Vietnamese
Türkçe
Turkish
Nederlands
Dutch
Italiano
Italian
SECURITY ARCHITECTURE
Engineered for Nation-State Adversaries
SANKET is built on Signal's independently audited libsignal and standard, peer-reviewed primitives, with post-quantum protection and AES-256 throughout.
Message Key Agreement
PQXDH
libsignal key agreement with a post-quantum Kyber prekey, protecting sessions against harvest-now-decrypt-later collection
Message Ratchet
Double Ratchet + SPQR
The Triple Ratchet: a fresh key for every message, forward secrecy and recovery after compromise, with a post-quantum ratchet alongside
Message Encryption
AES-256-CBC + HMAC-SHA256
Inside libsignal, one ciphertext for every recipient device
Groups
Per-Device Fan-Out
Pairwise libsignal sessions to every member device, so there is no group key to steal
File Encryption
AES-256-GCM
A fresh key for every file, delivered inside the libsignal message
Call Encryption
AES-256-GCM Frames + SRTP
Frame encryption plus SRTP AES-256-GCM, with five new frame keys every second
Transport Security
TLS 1.3 + Hybrid PQ
AES-256-GCM-only suites, X25519MLKEM768 offered first, certificate pinning in the apps
Device Authentication
Device Mutual TLS
A client certificate for every approved device, issued under your certificate authority
Device Lists
Signed by the Account
Senders verify the signed list, so the server cannot silently add a device
Private Key Storage
Hardware-Backed
Secure Enclave on iOS, StrongBox or the trusted execution environment on Android
Administrator Sign-In
FIDO2 Security Keys
Phishing-resistant WebAuthn keys verified by the installation itself
Releases
Ed25519-Signed
Freeze and rollback protection, verified before every install and upgrade
Server-Blind by Design
The server relays ciphertext and never holds the keys to messages, files, calls, reactions or encrypted broadcasts. Encryption and decryption happen on the participants' devices.
Threat Model - Who We Defend Against
Nation-State Signals Intelligence
End-to-end encryption with post-quantum PQXDH and SPQR, AES-256-GCM-only TLS with hybrid post-quantum key exchange, and forward secrecy for every message.
Compromised Server
The server never holds the keys to content, and signed device lists stop it adding a device that would receive copies of messages.
Rogue CA or Network Interception
Certificate pinning in the apps, device mutual TLS at the edge and AES-256-GCM-only transport suites.
Compromised Administrator Account
FIDO2 security keys for administrators, permission-scoped roles and a SHA-256 hash-chained audit log that can be verified and exported to your SIEM.
Supply-Chain and Rollback Attacks
Ed25519-signed releases with sequence numbers, expiry and a signed bill of materials; an installation refuses unsigned, expired or older releases.
Lost or Seized Device
Hardware-backed keys, an encrypted local database, instant revocation, lost mode and server-confirmed remote wipe.
Built on Signal's Independently Audited libsignal
Signal's libsignal library
Signal's official, independently audited implementation of the Signal Protocol, used without modification on iOS, Android, desktop and server
Published, peer-reviewed protocols
PQXDH, the Double Ratchet and SPQR, with published specifications and academic analysis
Standard primitives
AES-256-GCM, X25519, Ed25519, ECDSA P-256, SHA-256, HKDF, Argon2id and the ML-KEM family
Platform secure hardware
Apple Secure Enclave and Android StrongBox or the trusted execution environment for device keys
Audited-library rule
Every cryptographic library SANKET relies on is held to a rule of a published independent audit
Certification Pathway
DEPLOYMENT OPTIONS
Product Tiers
Sanket.Chat
The free private messaging app for iOS and Android, operated by Tosh Defence on Indian infrastructure.
Sanket.Work
A dedicated, whitelabel installation hosted in any region on any cloud you choose, with administrator control, your branding and desktop apps for your organisation.
Sanket.Enterprise
A customer-operated installation for defence, government, intelligence and critical infrastructure, on-premise or fully air-gapped.
WHY NOT A FOREIGN ALTERNATIVE?
Why SANKET?
“Your communications should never force you to surrender ownership. With SANKET, the control stays with you.”
INTEGRATION
Works With
DESIGNED FOR
Who It Serves
Proudly Made in India
Designed, built and supported in India by Tosh Defence, on audited open foundations. Deployable anywhere in the world, with no foreign runtime dependency in an air-gapped installation and source review available to customers under agreement.
Explore SANKET in depth
Go deeper into the security design, the sectors SANKET serves, how it compares and the public security whitepaper.
Ready to See SANKET in Action?
Schedule a live demonstration with our team, tailored to your operational requirements, wherever you are in the world.